Alpha Apex Group / Security Leadership Search

CISO Executive Search

Recruit security leadership around your business risks.

Alpha Apex Group helps organizations recruit a Chief Information Security Officer for their risk context and operating needs. We clarify the leadership mandate, team responsibilities, and executive relationships. Assess candidates for the judgment and experience required to connect security priorities with consequential business decisions.

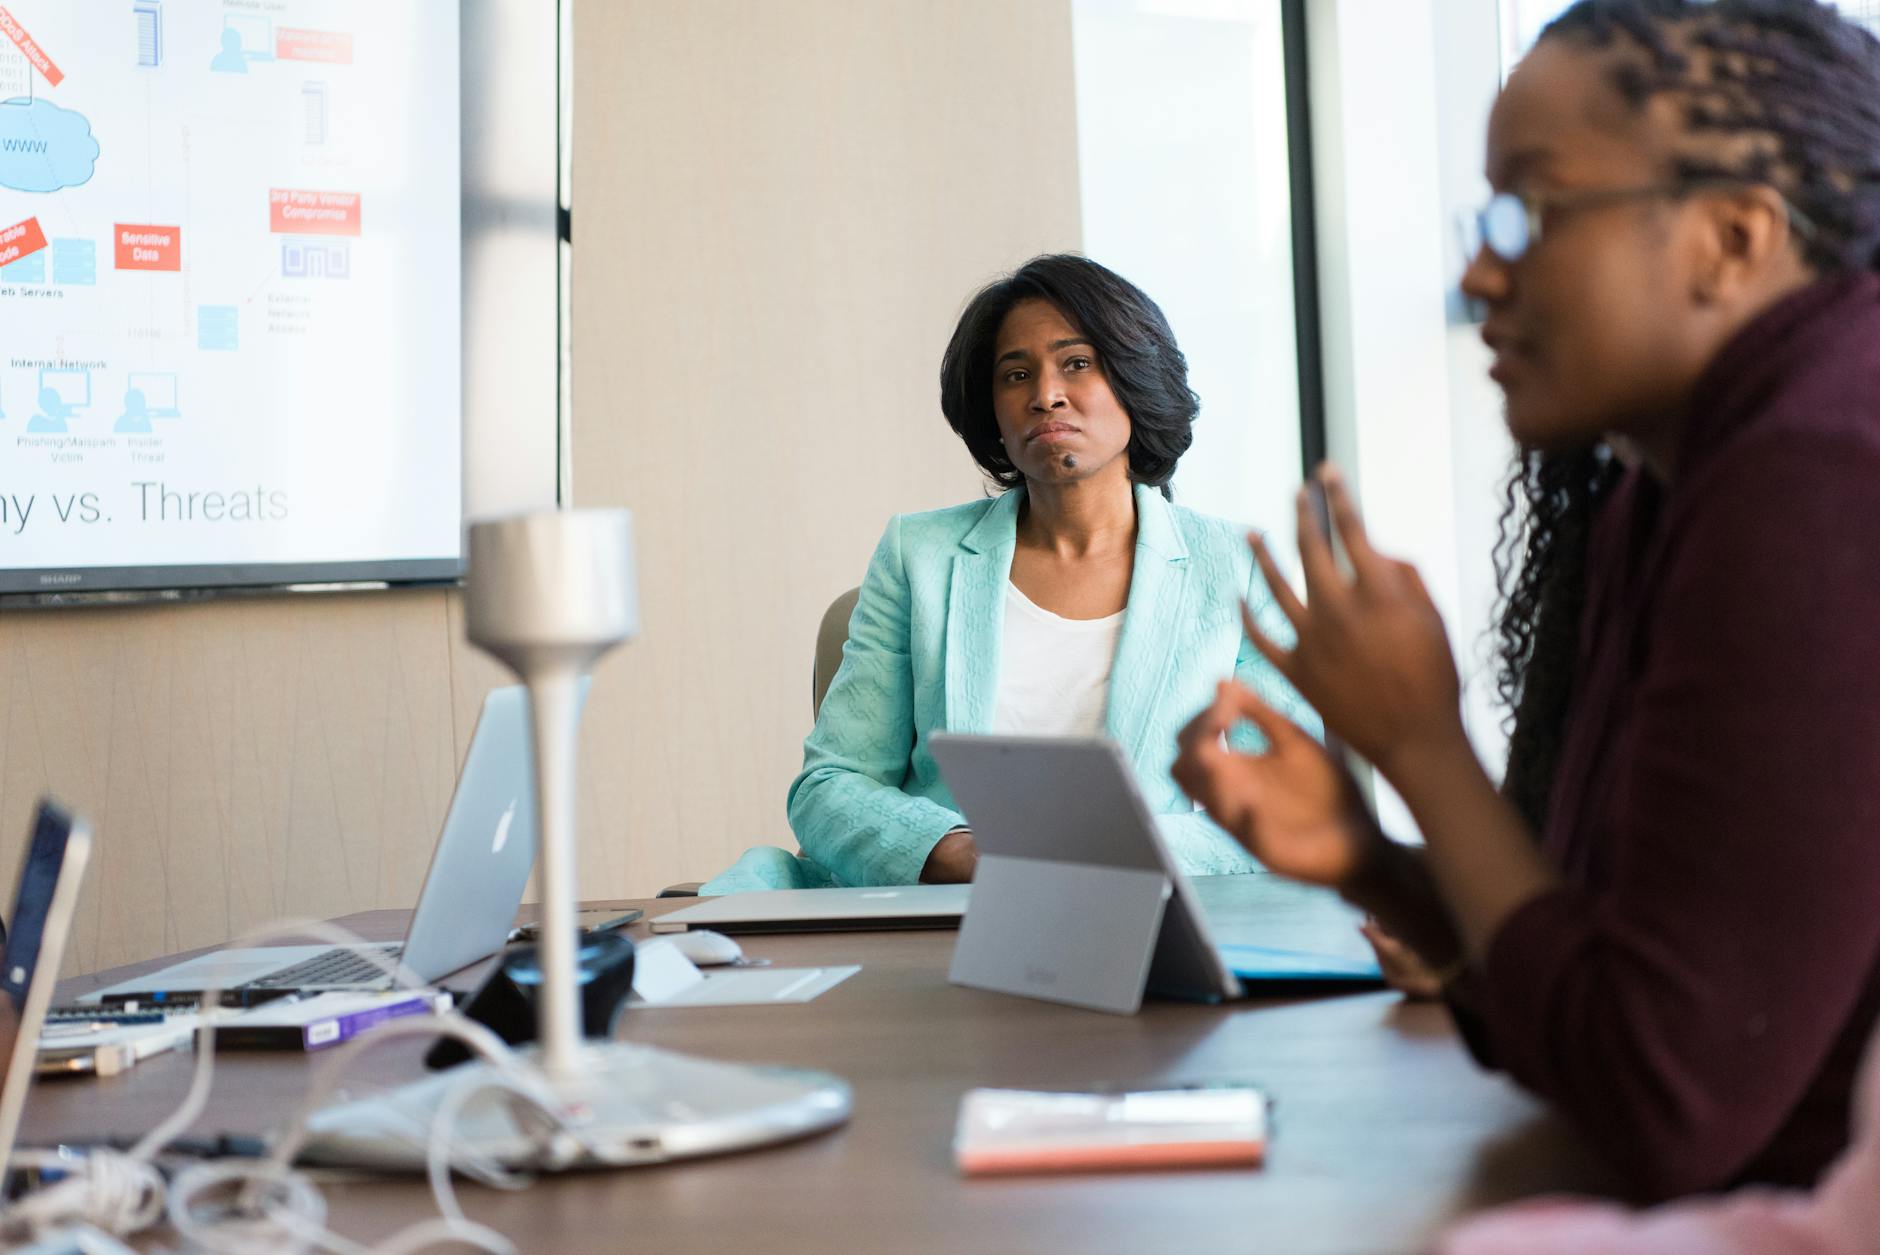
Professionals discussing a planning board during a business meeting.

Relevant judgment. Clear accountability. Practical security leadership.

Trusted by the best

01 / Your priorities

Define the security leadership mandate before choosing the profile.

A CISO appointment may follow growth, a change in business model, new ownership expectations, or a security function that needs stronger direction. Each situation creates a different leadership requirement. A candidate experienced in a large established organization may need substantial support in a smaller business, while a hands-on builder may be stepping into a different challenge when leading a complex enterprise team. The search should reflect the actual mandate.

Our CISO executive search work starts with the decisions the organization needs the leader to make and influence. Clarify the role’s authority, reporting line, resources, and relationships with technology and business leaders. Identify which capabilities must be established on arrival and where the team can provide depth. An honest brief helps candidates understand the opportunity and gives sponsors a consistent basis for comparing relevant experience.

Risk & priorities

Discuss the business context and the security decisions that need leadership attention. Ask candidates how they have chosen priorities when resources were constrained and expectations competed. Explore the information they used and how they explained the trade-offs. The assessment should show judgment relevant to your organization, without assuming that the most extensive program or largest budget represents the best fit.
Executive communication

Look for an ability to explain important security issues in terms decision-makers can use. Explore how candidates have worked with executives and boards, communicated uncertainty, and requested action or investment. Strong communication connects the issue with a clear decision and its implications. It should remain accurate while adapting the level of detail to the audience and the responsibility involved.

Team & execution

Define the team the CISO will inherit and the capability that needs to be built. Examine how candidates developed people, worked with external partners, and maintained accountability for delivery. Identify what they accomplished personally and what depended on an established infrastructure. The right leadership profile needs to match your resources and the balance between strategic direction and direct involvement in the work.

Business & partnership

Security leadership depends on relationships beyond the security function. Ask how the candidate worked with product, operations, technology, and other relevant leaders when priorities differed. Explore their approach to constructive challenge and practical cooperation. The search should assess whether the person can maintain clear expectations while understanding the operating constraints and decisions other leaders need to manage.

02 / CISO mandate

Make authority, responsibilities, and organizational interfaces explicit.

Enterprise security leadership

Define the scope of the CISO role within your organization rather than assume the title settles it. Clarify responsibility for security direction, team leadership, governance, and the relevant operating relationships. Explain how the role connects with technology, business functions, and other risk or control responsibilities. Identify the decisions the CISO owns, the decisions they advise on, and how disagreements are resolved. These arrangements affect both the candidate profile and the conditions for success.

Capability and technical depth around the role

A CISO should have the understanding needed to lead the mandate, but no single executive supplies every specialist capability. Review the expertise already available and the areas requiring further development. Where cloud security, threat intelligence, or other specific experience is relevant, explain how it connects to the work the leader must oversee. Distinguish executive judgment from hands-on specialist delivery. The search can then assess appropriate depth without turning the role into an unrealistic combination of every responsibility across the security function.

03 / Our approach

Create a consistent path from mandate to appointment.

01

Align the sponsors on the leadership requirement

Discuss the business priorities, current security organization, and reasons for the hire. Agree the outcomes expected from the appointment and the authority and support available. Clarify reporting relationships, executive exposure, location expectations, and compensation parameters. Identify essential capabilities and separate them from preferences. This work gives interviewers a shared view of the role and reduces the risk that candidates encounter conflicting versions of the opportunity during the assessment process.

02

Research the relevant leadership market

Identify environments where candidates could have developed comparable judgment and experience. Consider business complexity, organizational maturity, stakeholder relationships, and the resources available in previous roles. Explain the opportunity through the mandate and explore the candidate’s motivation for a move. Use market feedback to test assumptions about scope and availability. Keep changes to the profile deliberate and agreed with the sponsors so the search remains centered on the organization’s actual needs.

03

Assess decisions, leadership, and contribution

Structure conversations around the agreed priorities and ask candidates to explain specific situations. Explore the decisions they made, the information available, and the people involved. Examine how they developed capability and handled difficult executive relationships. Distinguish the candidate’s own contribution from the achievements of the wider team. References, where appropriate and with consent, can add context to responsibilities and working style. The comparison should include both demonstrated strengths and areas requiring support.

04

Prepare the appointment and first-stage priorities

Resolve outstanding questions about scope, authority, resources, and expectations before the appointment. Give the candidate an accurate picture of the work and the challenges ahead. Plan relevant introductions and access to context, then agree how early priorities will be discussed. The new CISO needs room to form an informed view while understanding urgent responsibilities. A practical transition connects the recruitment mandate with the organization’s real decision-making and operating arrangements.

Close-up of connected server equipment inside a rack.

Examine the judgment behind the security leadership experience.

04 / Candidate assessment

Look at how the candidate leads when the choices are difficult.

A useful assessment explores relevant decisions, execution, and relationships rather than relying on job titles, presentation style, or a list of technologies.

Prioritization with incomplete information

Ask the candidate to describe a consequential security decision where the answer was not obvious. Explore the alternatives, assumptions, and information they considered. How did they decide what needed attention first, and how did they explain the implications to others? Look for an ability to distinguish what was known from what remained uncertain. The example should help sponsors understand the candidate’s reasoning and its relevance to the choices the incoming CISO will face.

Leadership through pressure and changing conditions

Explore a situation in which the candidate needed to coordinate people and decisions under pressure. Ask about their role, the preparation available, and how they worked with other leaders. Examine what they learned and what changed afterward. Keep the discussion focused on leadership contribution and appropriate, non-sensitive examples. An impressive account of a difficult event is less useful than a clear explanation of responsibilities, judgment, coordination, and follow-through.

Building a capable and accountable function

Discuss the team the candidate inherited and the improvements they chose to make. Explore how they assessed capability, developed leaders, and decided where external support was appropriate. Ask how they kept priorities visible and addressed delivery problems. The circumstances matter: a candidate who operated with extensive resources may approach your environment differently from one who built a function with a small team. Assess that fit alongside the evidence of results and learning.

05 / Your business

Match the CISO to the organization’s operating context.

Businesses hiring their first dedicated CISO

A first CISO may need to establish the role’s relationships and operating routines as well as lead the security agenda. Clarify sponsorship and the authority the organization is prepared to provide. Look for experience building a practical starting point with realistic resources. The appointment should not be expected to compensate for unresolved leadership decisions about ownership or investment that remain outside the new hire’s control.

Enterprises strengthening established security leadership

An established function may need a leader who can understand the existing program, identify meaningful gaps, and guide the next stage. Define what should continue and what requires change. Assess how candidates have improved organizations without assuming everything needs replacement. The search should consider the complexity of the team and stakeholder relationships, along with the candidate’s ability to make choices and maintain continuity while introducing improvements.

Organizations undergoing technology or business change

A changing business model, major technology program, or expanding operating footprint can alter the leadership requirement. Explain the decisions the CISO will need to influence and the other teams involved. Look for evidence of working through change while maintaining a coherent set of priorities. Avoid treating experience with a particular initiative as sufficient on its own; examine what the candidate actually owned and how they worked with the wider business.

Leadership teams seeking stronger security communication

The need may include a clearer relationship between the security function and executive decision-making. Define what leaders currently find difficult to understand or act on. Assess candidates through examples of explaining trade-offs, presenting uncertainty, and obtaining decisions from senior stakeholders. Strong communication should make the underlying issue more usable without hiding important limitations or reducing the role to producing reports that do not support a clear action.

06 / Common questions

Prepare a focused brief for the security leadership search.

Answers about scope, experience, reporting relationships, confidentiality, and the transition into the CISO role.

Discuss your CISO search →
What should a CISO search brief include?

Include the reason for hiring, the business context, the current security team, and the outcomes expected from the role. Clarify reporting relationships, decision authority, executive exposure, and resources. Identify the technical or sector experience that is essential and explain why. Compensation parameters, location expectations, and confidentiality requirements also shape the search. A useful brief describes the work and the conditions around it rather than rely on the title alone.

Where should the CISO report?

The reporting arrangement should be considered in the context of your organization’s structure, governance, and expectations for the role. Clarify how the CISO will communicate with relevant executives and how decisions or disagreements will be handled. The search needs an agreed arrangement that candidates can evaluate. Avoid leaving fundamental questions about authority or access unresolved until the incoming leader is expected to negotiate them after joining.

Does the candidate need experience in our sector?

Sector experience can be important when the role requires immediate understanding of specialized operating conditions. It should still be examined alongside comparable complexity, leadership responsibilities, and the actual mandate. Decide what must be known on arrival and what can be learned with support. A familiar industry background does not replace evidence of judgment, execution, and the ability to work effectively with the people who will shape the role.

How should we evaluate technical credentials?

Credentials and technical experience can inform the assessment, but they should be connected to the responsibilities of the vacancy. Ask candidates to explain how they applied relevant knowledge in decisions and leadership work. Consider the expertise available elsewhere in the team and the depth the CISO needs personally. The assessment should establish the appropriate capability for the mandate, rather than treat a credential or tool list as a complete proxy for leadership fit.

Can the search be conducted confidentially?

Discuss confidentiality requirements before outreach begins. Agree who is aware of the search, what can be shared at each stage, and how the opportunity will be described accurately. Candidates may also need discretion with their current employers. Establish clear communication arrangements and share sensitive internal information only through appropriate agreed channels when needed. The process should allow both sides to assess the opportunity responsibly without assuming every detail must be disclosed immediately.

How long will a CISO executive search take?

Timing depends on the mandate, candidate market, location, compensation, assessment process, and availability of decision-makers. Notice periods and transition arrangements can affect the start date after acceptance. Agree a practical plan and review progress against the actual market response. Coordinated interviews and a clear brief help keep the search focused. The likely schedule should be discussed for the specific appointment rather than presented as identical for every organization.

What should we assess in a first-time CISO candidate?

Examine which responsibilities the candidate has already handled and where the step into the role would be greatest. A senior security leader may bring relevant experience without having held the CISO title. Explore executive communication, people leadership, breadth of judgment, and responsibility for difficult decisions. Consider the support available from the sponsor and existing team. The assessment should make both the candidate’s strengths and the transition needs explicit.

How can we support the new CISO’s transition?

Provide the context and relationships needed to understand the organization, including relevant priorities and decisions already made. Clarify urgent responsibilities while allowing time for the leader to develop an informed view. Confirm authority, resources, and review points with the sponsor. The transition should support a shared understanding of the mandate and create a practical way to discuss new findings or assumptions that need adjustment after the appointment.

Before day one

Give your next CISO a clear starting point.

Prepare the priorities, relationships, and decision arrangements that connect the appointment to the work ahead.

Align the immediate mandate

Confirm the urgent responsibilities and the areas the CISO should first review. Explain which expectations are established and which decisions remain open for the incoming leader’s assessment.

Prepare executive relationships

Plan introductions to the leaders and teams whose participation will matter. Clarify how they work with the security function and where the CISO can obtain context or resolve questions.

Review early findings

Agree a rhythm for discussing observations, priorities, and support needs. Maintain clear accountability while allowing the mandate to be informed by what the leader learns about the organization.